Evidence and audit
Every step, with date, owner and fingerprint.
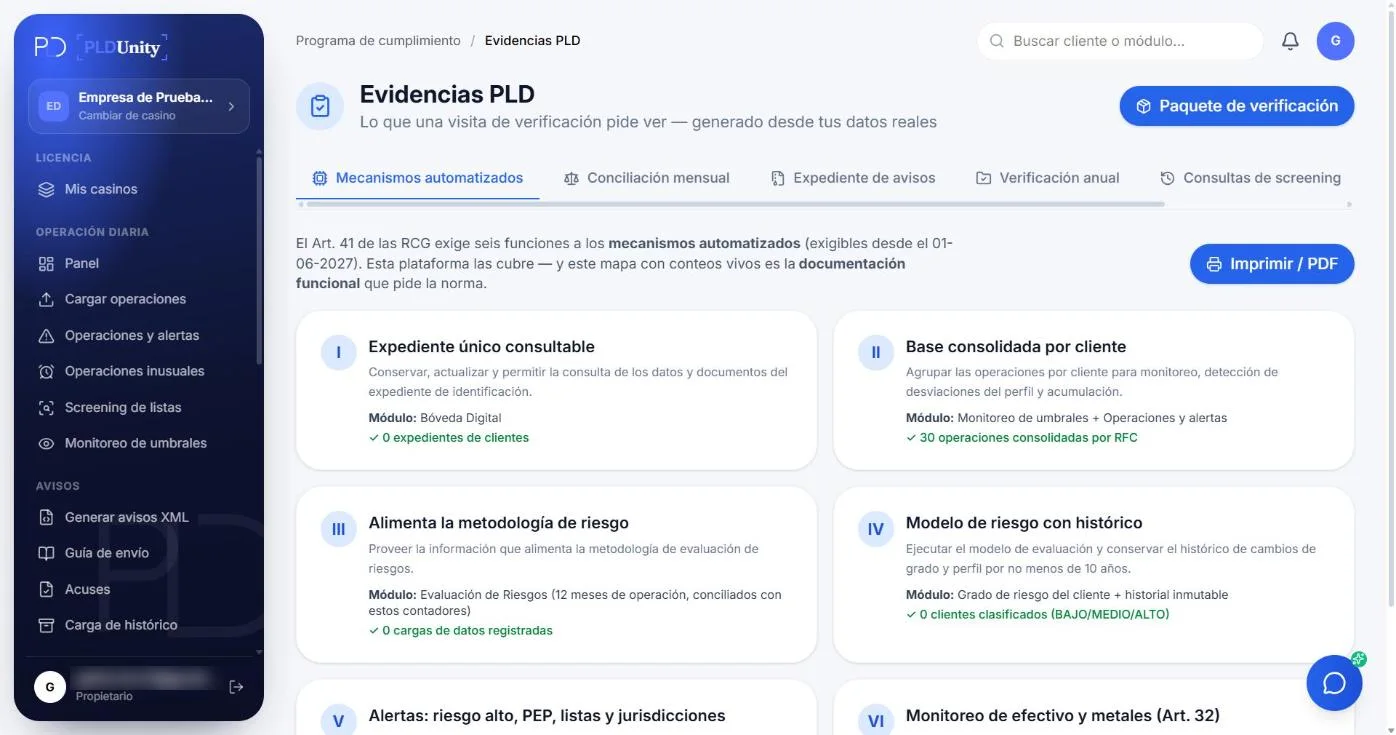
An audit log of every action, acknowledgments linked to their report, SHA-256 fingerprints on XML files and exports, and an audit package ready for the inspection.
OPERATIONAL SUITE · LFPIORPI COMPLIANCE
Every monthly compliance task, synchronized in one cockpit.
Explore how each module works interactively. Operations feed threshold tracking, screening, risk assessment and XML notices without duplicate manual entry.
Evidence & Audit Vault
MODULE CAPABILITIES
What it does
- 01Feature
A log only the server can write
Uploads, reports, role changes and exports are recorded with date, time and user.
- 02Feature
Linked acknowledgments
The SAT portal acknowledgment is stored with the report and the period.
- 03Feature
Integrity fingerprint
Report XML files, acknowledgments and export packages carry a SHA-256 fingerprint.
- 04Feature
Self-assessment of 16 obligations
Check your program against the law's obligations and generate the audit package.
- 05Feature
10-year retention
A complete, portable export, in parts, whenever you ask.
- 06Feature
In-system AML Compliance Manual generator
Drafts and versions your official AML Policies and Procedures Manual populated with your entity profile and EBR methodology.
REGULATORY & OPERATIONAL GUIDE
Compliance Guidelines for Evidence and audit
Essential LFPIORPI obligations, identification criteria, and supervisory rules applicable to this activity.
In an inspection it is not enough to comply: you have to prove it. This module brings together the evidence that is usually scattered across emails, folders and spreadsheets.
MODULE FREQUENTLY ASKED QUESTIONS
Frequently asked questions
What is included in the Audit & Evidence Package?
It compiles a structured, indexed dossier containing everything an external auditor or SAT/UIF inspector requests: SPPLD registration proof, Compliance Officer appointment, active Compliance Manual, EBR methodology and matrix, XML notices and SAT receipts, SHA-256 hashed KYC files, watchlist screening logs, alert adjudications, and annual training certificates.
How does read-only access work for the External Auditor (mandatory in 2028)?
You can grant your external auditor a time-bound, read-only role. They can inspect KYC files, verify cryptographic hashes, review EBR calculations, and export audit samples without being able to modify any operational data.
How does it help us respond to a SAT inspection or information request on deadline?
When a regulatory request arrives, you can filter by filing period, branch, or client list and export a complete, indexed evidence bundle with timestamps and integrity hashes in minutes.
How does it enforce the 10-year retention period under the LFPIORPI reform?
The module tracks the retention clock for every KYC document, XML filing, and SAT receipt from its creation date, ensuring tamper-proof availability across the full 10-year statutory period.
Can any user or administrator edit or delete entries in the audit log?
No. The audit trail is strictly append-only: every event records the user, role, UTC timestamp, and IP address, and cannot be altered or deleted by anyone.
How does the 16-obligation Article 18 self-assessment work?
The dashboard scores your organization's real-time readiness across all 16 statutory obligations under Article 18—highlighting any gap (such as a missing SAT receipt or overdue training) before an inspection occurs.
30-DAY FREE TRIAL · NO CREDIT CARD
Put the Evidence and audit module to work with your own data.
Start your 30-day free trial with your own transactions or schedule a 30-minute walkthrough with BDUnity's compliance specialists.