Team and role permissions
Everyone sees and does what they should.
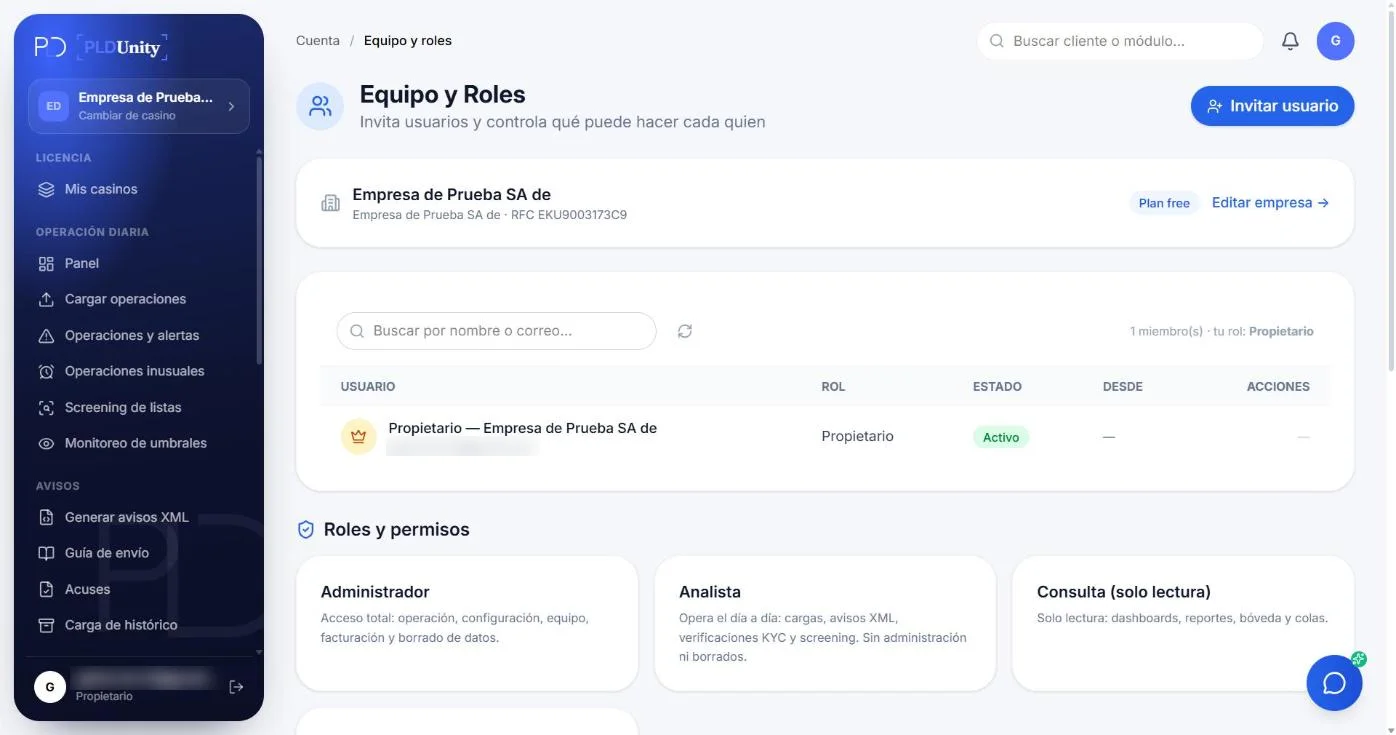
Owner, administrator, analyst, read-only and external auditor with an expiry date: role-based permissions, two-factor authentication and a log of every change.
OPERATIONAL SUITE · LFPIORPI COMPLIANCE
Every monthly compliance task, synchronized in one cockpit.
Explore how each module works interactively. Operations feed threshold tracking, screening, risk assessment and XML notices without duplicate manual entry.
Team Permissions
MODULE CAPABILITIES
What it does
- 01Feature
Roles
Owner, administrator, analyst, read-only and external auditor (read-only, with an expiry date).
- 02Feature
Segregation of duties
Whoever uploads doesn't have to be whoever reviews or files.
- 03Feature
Two-factor authentication (TOTP)
Mandatory for administrators and available to every user.
- 04Feature
Invitations by email
Add or remove people from your company in a minute; every change goes into the audit log.
- 05Feature
Multi-entity console & permit-holder oversight
Switch across multiple RFCs or oversee operating subsidiaries from a parent account with strict database isolation per tax ID.
- 06Feature
Forensic session & access audit trail
Logs every sign-in, IP address, role change, and sensitive document view inside an immutable 10-year security ledger.
REGULATORY & OPERATIONAL GUIDE
Compliance Guidelines for Team and role permissions
Essential LFPIORPI obligations, identification criteria, and supervisory rules applicable to this activity.
Segregation of duties reduces errors and makes clear who is responsible for each step. User limits depend on the plan: 1 on Free, 3 to 10 on Pro and unlimited on Enterprise.
MODULE FREQUENTLY ASKED QUESTIONS
Frequently asked questions
Which predefined compliance roles exist and what can each role do?
Roles map directly to AML governance: Admin/Compliance Officer (full control, EBR configuration, alert adjudication, XML generation), AML Analyst (document review and monitoring without altering settings), Cashier/Branch (restricted front-desk capture), and External Auditor (temporary read-only access).
Can I manage multiple legal entities or RFCs from a single login?
Yes. A Compliance Officer or corporate group can switch seamlessly between multiple RFCs from the top selector while keeping databases, KYC vaults, and audit trails strictly segregated per legal entity.
Can we restrict a user so they only see transactions from their own branch or location?
Yes. Users can be scoped to a specific branch, dealership, or gaming hall so they only capture and view local operations, while the Compliance Officer sees consolidated national activity.
What happens to the audit trail when an employee leaves and we revoke their access?
Deactivating a user immediately terminates their active sessions, while preserving all of their historical actions, adjudications, and training certificates inside the immutable 10-year audit log.
Are login timestamps and IP addresses logged for every team member?
Yes. Every sign-in, permission change, document view, or XML export is logged with exact timestamp, user ID, and IP address for internal security and regulatory auditing.
How does two-factor authentication (2FA / TOTP) protect user accounts?
Users can enable TOTP two-factor authentication with standard authenticator apps (Google Authenticator, Microsoft Authenticator, Authy) to protect KYC vaults and XML exports.
30-DAY FREE TRIAL · NO CREDIT CARD
Put the Team and role permissions module to work with your own data.
Start your 30-day free trial with your own transactions or schedule a 30-minute walkthrough with BDUnity's compliance specialists.